Overview
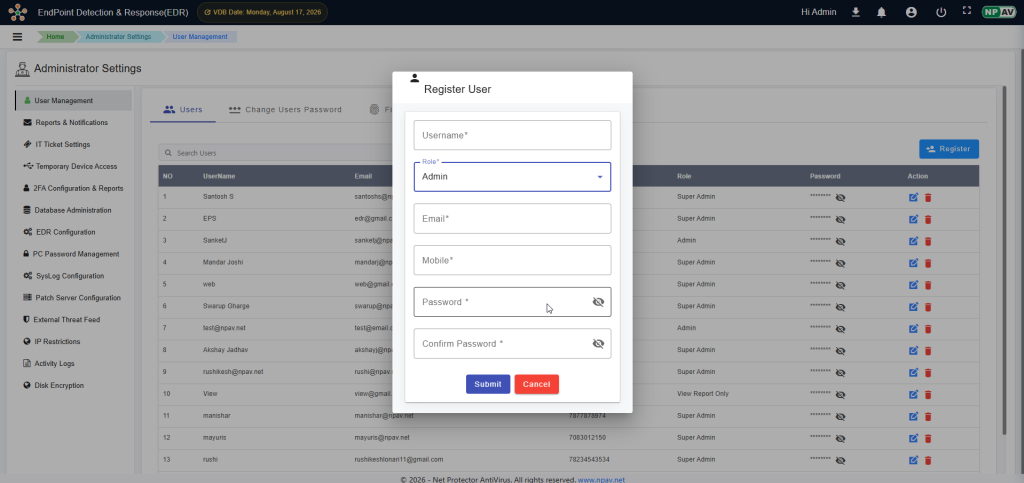
NPAV EDR provides Role-Based Access Control (RBAC) to ensure that administrators have access only to the features and operations appropriate to their assigned roles. This helps protect security configurations, prevent unauthorized changes, and maintain accountability across the management console.
Available Roles
- Super Admin: Provides complete access to the NPAV EDR Management Console, including security policies, endpoint management, user and role administration, configuration, monitoring, reporting, and administrative actions.
- Admin: Provides access to day-to-day endpoint security management, monitoring, policy management, and reporting based on the permissions assigned to the administrator. Administrative privileges can be restricted from critical system-level operations.
- Viewer: Provides read-only access to the management console. Viewers can monitor endpoints, security events, dashboards, and reports but cannot modify policies, configurations, or perform administrative actions.
Key Benefits
- Granular access control based on user roles.
- Prevents unauthorized configuration changes.
- Separates administrative and monitoring responsibilities.
- Supports secure and accountable endpoint management.
- Provides centralized user access management through the NPAV EDR Management Console.
